A growing number of Facebook users are reporting repeated “partner request” emails linked to a suspected Meta Business Suite Email Issue, raising concerns over a possible notification system anomaly or abuse of the platform’s partner-sharing feature.
Over the past two months, multiple users say they have received the same email dozens of times—some reporting more than 50 identical messages—sparking confusion and suspicion across online communities.
Users say the emails keep coming
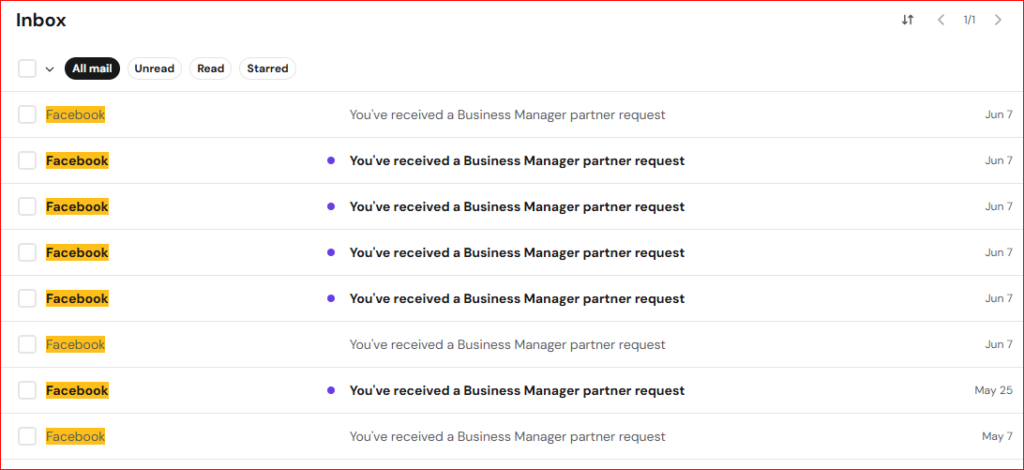
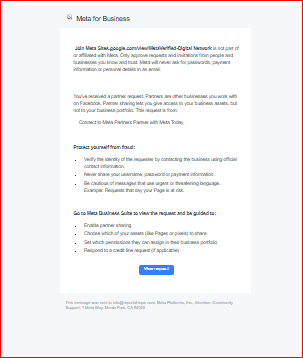
The emails, which appear to be tied to Meta Business Suite workflows, notify users of “partner requests” that allow businesses to share access to assets such as Pages, ad accounts, or pixels.
A Facebook user asked, ” Dear Meta Business, is your platform hacked?” referring to the repeated emails he had received from the platform.
While the content of the emails appears consistent with Meta’s standard business security language, the volume and repetition have alarmed users who say they did not initiate or approve any such requests.
Across Facebook posts discussing the issue, several users confirmed similar experiences, suggesting the problem may be more widespread than isolated incidents.
Emails originate from official Meta domain — but raise questions
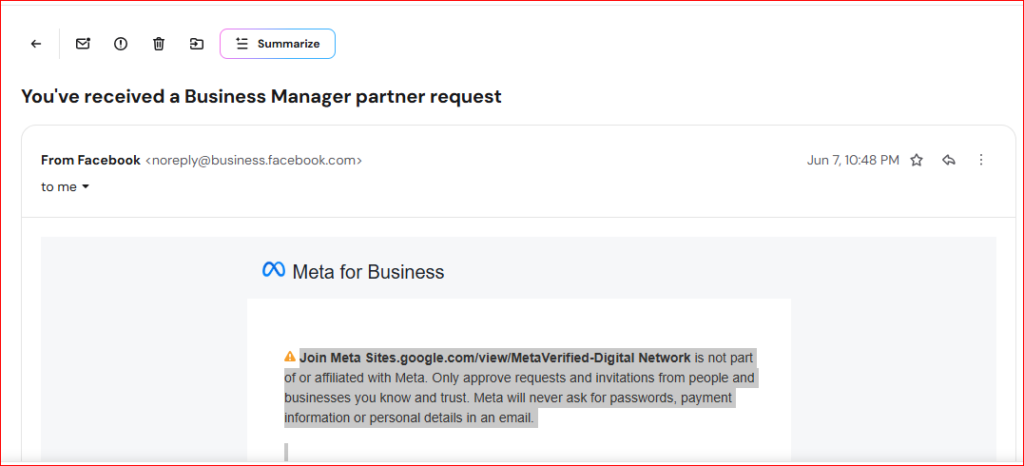
Unlike typical phishing attempts that rely on spoofed or unrelated domains, these messages are being sent from a legitimate Meta address:
This detail has complicated the situation. On one hand, the domain suggests the messages are authentic system-generated notifications from Meta’s infrastructure. On the other, users argue that the repeated, unsolicited nature of the emails feels abnormal for standard Business Suite activity.
Cybersecurity observers note that even legitimate email channels can be misused or triggered excessively if a system is misconfigured or if automated partner-request features are being exploited at scale.
Possible causes of Meta Business Suite Email Issue: glitch, misuse, or notification abuse
At this stage, there is no official explanation from Meta as to if this is a Meta Business Suite Email Issue. However, three possibilities are being discussed by users and analysts:
- A malfunction or bug within Meta Business Suite’s notification system
- Abuse of the partner request feature to trigger repeated notifications
- Or a broader system design issue allowing automated or spam-like partner requests
The consistency of the reports across unrelated users has led some to suspect a platform-level issue rather than isolated account activity.
Why the issue matters for Meta’s business ecosystem
If the emails are the result of a system-level fault or abuse of Meta’s partner-sharing tools, it could raise broader concerns for businesses relying on Facebook and Instagram for advertising, analytics, and page management.
Meta’s Business Suite and Business Manager tools are widely used by small and large organizations to manage digital assets. Any vulnerability in notification integrity or partner access workflows could potentially affect trust in the ecosystem.
Security guidance for users
Until Meta provides clarification, users are advised to:
- Avoid clicking links inside unexpected partner request emails
- Confirm all requests directly within Meta Business Suite or the Facebook app
- Never enter login details outside official Meta domains
- Report repeated or suspicious messages through Meta’s security tools
- Enable two-factor authentication on all accounts
Growing calls for clarification from Meta
As reports continue to surface, users are calling for Meta to investigate whether the issue stems from a technical bug or misuse of its partner-request system.
So far, Meta has not issued a public statement addressing the recurring emails or their unusually high frequency.
For now, the situation remains unresolved—but the combination of official-domain emails, repeated delivery, and widespread user reports has been enough to raise questions about the stability and security of Meta’s business communication systems.
WIRED.Africa will continue tracking developments as more information emerges.

The WIRED.Africa's Press Desk delivers breaking news, official announcements, and timely updates on technology, business, innovation, and digital policy. Stories published under this byline are produced through the collaborative efforts of the editorial team and trusted news sources.